rss
twitter
    Find out what I'm doing, Follow Me :)

Wednesday, December 22, 2010

Special tips about Magento Customization and Magento Theme Development

This post is all about Magento customization and Magento theme development with website applications development. Today web services are growing very fast and many new programming language and framework used to create dynamic websites.

Many business persons use ecommerce website to provide unique web solutions to their customers. People can buy or sell product online through ecommerce web site and get response through the website. Website developer use Magento software to develop ecommerce website.

Magento is an open source web applications software used to develop ecommerce projects and shopping cart solution. Website programmers develop themes for the Magento ecommerce platform, which provide flexible web solutions to create new projects.

If you want to develop ecommerce magento based website and want to boost your business returns, then it is mandatory to build up an e-commerce website. Magento e-Commerce is the new technology arrives for ecommerce development and shopping cart solution, and the latest technology available. Magento will help you to create online store, online shopping cart with Magento CMS and customization.

Magento theme development used to get complete ecommerce solutions for online shopping cart web services. You can easily understand functionality of an Online Store with Magento development. The Magento Commerce Platform combines the flexibility of open-source technology with industry leading features to provide merchants unprecedented control over online store operations and get the online sales booming

Tuesday, December 14, 2010

Hire PHP Programmer – Web Development – Website Design Company

PHP is one of the fastest growing web scripting languages on the Internet today, and for this reason this languages is globally used to develop website.

Web Development in PHP is becoming increasingly popular in website development industry because of PHP is open source language. Open source technology is used to make CMS web development and e-commerce website solutions. PHP web programming is easily under-stable and easy to run on any OS platform.

In this time, many business services are based on ecommerce system and they need to build a online sells management system and this systems can be easily developed in PHP. Magento, Joomla, Wordpress, OsCommerce etc. are most popular CMS platforms, which are totally based on PHP.

If you have business, which is related to online services, then you need to hire PHP programmer to build your ecommerce website. In India many website design company provide web development services but you have to select perfect web Development Company that make accurate website for your business.

PHP web development company in India offer several web applications services like web design, web development PSD conversion and search engine optimization services to help your business. Web Applications Development Company associated with dedicated PHP developer, web designer and SEO experts to perform unique web solutions according to clients’ requirement.

Online selling web portal need well web applications systems, which makes flexible environment on internet for user. PHP has all major parameters, which are used to develop data driven web applications, and due to this reason, PHP is highly popular in the world. If you are going to make new ecommerce web applications they you can make it easily with PHP.

Thursday, July 1, 2010

How to add new layout template for Magento

Many times we need to add new layout skeleton rather then 2colums-left, 2columns-right, 1column and 3columns. Here is the way how we can add more layout structures.


You can make modification directly in app/code/core/Page/etc/config.xml but if you don’t want to touch core file, I recommend you to follow these steps:

Create config.xml under app/code/local/Magestore/Page/etc

<?xml version="1.0" encoding="utf-8"?>
<config>
<modules>
<Magestore_Page>
<version>0.1.0</version>
</Magestore_Page>
</modules>
<global>
<page>
<layouts>
<three_columns_cms module="page" translate="label">
<label>3 columns for cms page</label>
<template>page/3columns-cms.phtml</template>
<layout_handle>page_three_columns_cms</layout_handle>
</three_columns_cms>
</layouts>
</page>
</global>
</config>

Now, open app/etc/modules and create file Magestore_Page.xml

<?xml version="1.0"?>
<config>
<modules>
<Magestore_Page>
<active>true</active>
<codePool>local</codePool>
</Magestore_Page>
</modules>
</config>
 

You have to create a file named '3columns-cms.phtml' under app/design/frontend/[YOUR_PACKAGE]/[YOUR_THEME]/template/page.

Now, log in your admin, go to Cms -> Manage pages, click Add new page. In Custom Design tab, you can find new layout you just created:

Saturday, June 19, 2010

Whats New in Magento 1.4.1.0

Improvements

  • Added ability to use static URLs for media in WYSIWYG or image browser. Added ability to enable parsing store, skin and media directives on catalog frontend.
  • URL rewrites history: ability to auto-generate custom rewrite with redirect from old to new URL when changing product URL-key
  • Added ability to exclude a category from navigation menu
  • Various improvements in system configuration UI. Introduced ability to make actual configuration structure to be independent on the system.xml structure
  • Added "Only X left" inventory feature
  • Implemented Centinel functionality in iphone theme
  • Upgraded TinyMCE to v.3.3.2
  • Improved PayPal integration, includes:
    * Recurring payment profiles entity and purchasing of "subscription" products. In checkout they are treated as "nominal" items.
    * Billing agreements
    * "Pending Review" order state, "Pending Review" and "Suspected Fraud" order statuses and logic related with this. Triggers by PayPal IPR, FMF and Unilateral payments.
    * Functionality of transactions listing/searching and fetching from gateway
    * Fetching PayPal settlement reports via SFTP
    * Various improvements of PayPal integration on the frontend and admin UI
  • Added notice about creating offline creditmemo from order view page.
  • Added getter for recurring payment methods in payment helper.
  • Implemented abstract block ability to have arbitrary groups of child blocks and a method that returns such a group. Implemented a method that fetches data from child block by specified alias.
  • Implemented ability to specify "sort_order" instead of "before" and "after" in the totals declaration. All nominal totals declaration utilize "sort_order"
  • Added getter for specified object data by key in core/template block: method getObjectData()
  • Defined payment methods grouping, implemented getter for payment method list (with option to group them). Added ability to render grouped options in the "select" grid filter.
  • Moneybookers: utilized the payment methods grouping for all its methods; removed redundant "translate" attribute in the methods definition in config.
  • Utilized payment methods grouping for PayPal peyment methods.
  • Added more verbosity to PayPal NVP and IPN debugging

Changes

  • Sales module database structure changed from EAV into flat tables
  • Product custom URL rewrites redirect to SEF URL, rather than to catalog/product/view/id/
  • Reimplemented frontend top menu rendering logic (cross-browser and usability improvements)
  • Reviewed logic of the sales reports: Orders, Tax, Invoiced, Shipping, Refunds, Coupons
  • Reimplemented bestsellers report
  • Implemented 3D Secure validation for Maestro International and JCB cards
  • Changed Shopping cart methods output (top + bottom): removed
  • Moved the Payflow Pro payment method to PayPal module
  • Refactored sales/service_quote model: instead of submit() method the submitAll() should be used. It can submit nominal items separately from the order. The methods for submitting nominal items and order separately - are available as well.
  • Refactored onepage checkout model to use the new method sales/service_quote::submitAll(), added recurring profiles and billing agreements passing through the process until the success page
  • Utilized child blocks grouping to improve flexibility of rendering additional information in catalog/product/view template. The group is called "detailed_info"; any block from layout may insert itself to this group.
  • Removed redundant wrappers hard-coded into some catalog templates. Template of parent block is responsible for wrapping.
  • Refactored onepage checkout success block and template: simplified fetching related checkout information, added ability to render billing agreement and recurring profiles that might be created with the payment placement.

Saturday, June 5, 2010

Google Analytics code bug in Magento 1.4.0.1

We just released a site based on the latest community release of Magento 1.4.0.1. All went well until the point when we enabled Google Analytics for the site.

Firebug was showing an error: _gaq is not defined

google analytics error in magento 1.4.0.1

So there was a variable issue with the extra javascript analytics code inserted by Magento. A quick google search revealed that this issue was already reported in the Magento bug tracker and a solution/workaround provided.

The problem is in file: app/code/core/Mage/GoogleAnalytics/Block/Ga.php around line 170. Adding: var _gaq = _gaq || []; fixes the issue.

Easy fix, however, this sort of bug is something that shouldn’t have slipped through testing and quality control.

Friday, May 28, 2010

CSS In Magento

The first thing that you need to do with Magento is famililarise yourself with the CSS files, as you will be using these an awful lot. There are 7 different files in total, so you need to know what is located where and the things you will need to edit.

Most of the editing is done in the "boxes.css" file. All of the css files are located in ".../skin/frontend/YOUR_THEME/YOUR_THEME/css". If you have not changed the name of the theme or created a new one then it will be called "default" (".../skin/frontend/default/default/css") If you wish to change the colours or settings of any forms, tables, menus, buttons, error messages; then this is the place to be.

Ten Tips for Keeping your Magento Store Secure

Are you worried about the security of your Magento store? Magento has a number of built-in security features aimed at keeping you safe, but there are some steps you can take to make your site even more secure. Follow this ten-point security policy to protect your site from hackers and security breaches.

1. Choose a secure password

When you're choosing your Magento site's administrator passwords, choose wisely. Depending on your configuration and permissions, this password may give access to customer information and credit card data. This is probably review for most readers, but here are some guidelines for creating a really secure password:

Bigger is better. Use at least 10 characters.
Mix upper and lower case, punctuation, and numbers.
Making your password phonetic can make it easier to remember and type quickly.

2. Require HTTPS/SSL for all pages with logins

Each time you send data over an unencrypted connection you run a risk of this data being intercepted by an unwanted third-party. Login credentials are no exception. To minimize the risk of your username and password landing in unscrupulous hands, always send it over a secure connection. By always sending your login information over an encrypted connection, hackers are limited to expensive and extremely difficult brute-force attacks.

How to require HTTPS/SLL in Magento
In Magento you can require secure logins by selecting "yes" for both "Use Secure URLs in Frontend" and "Use Secure URLs in Admin" by going to the "Secure" section of the "Web" tab in the system configuration. In order to access the system configuration, go to the "System" menu and select "Configuration."
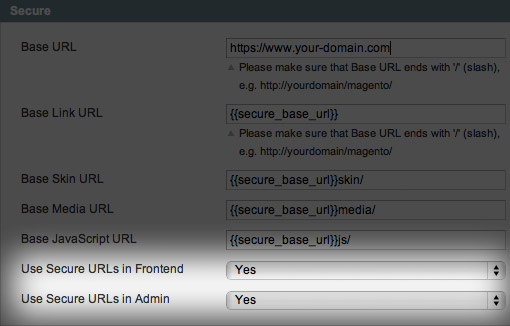
Magento Web Configuration Screenshot
Set "Use Secure URLs" to "yes" for both the frontend and admin

3. Don't use your Magento password for anything else

Do not use your Magento password with any other web services (such as email) or any other sites (such as Twitter, Facebook, Flickr, etc.). Third-party sites may not require or even support HTTPS/SSL to login, breaking rule number two. In the event that a third-party website is hacked, your password may be vulnerable.

4. Use a custom admin path

By default, you access your Magento admin panel by going to your-site.com/admin. Having the path to your admin panel path easily guessable means that someone or something (i.e. a password-guessing robot) can snoop around and try to guess your password. By having your admin path be a secret code word instead of the default /admin, you can prevent users from guessing your password or using it if they do somehow get a hold of your password.

How NOT to change your Magento admin path
Tucked in the "admin" section of the system configuration, the "Admin Base URL" setting looks like it offers the ability to set a custom admin URL and choose whether to use that custom URL or not. But BEWARE: this setting will break Magento by preventing you from accessing the admin panel (I've tested this and found this to be true as of Magento 1.4.0.1 and earlier).
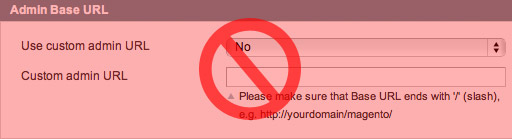
Magento Web Configuration Screenshot

BEWARE: Do not use the admin base URL settings; it will break your site.

How to change your Magento admin path
Although the setting does not work, there is an easy way to change your Magento admin path.

Locate /app/etc/local.xml
Find <![CDATA[admin]]> and replace 'admin' with the path you would like to use

So if your local.xml file says <![CDATA[drawbridge]]>, your admin path will be /drawbridge.

5. Close email loopholes

Magento has a really convenient feature that allows administrators to reset their password if forgotten. In order to reset your password, you need to know the email account associated with the account. Then you need access to that email account to retrieve the new password. First, choose an email address that is not publicly known. Second, make sure the password for your email account is secure. Third, make sure that if your email account has a security question that allows you to reset your password, you choose a question and answer that is so obscure that it would be impossible to guess.

6. Use secure FTP

Guessing or intercepting FTP passwords is probably one of the number one ways sites get "hacked." In order to prevent unauthorized access to your sites FTP, use secure passwords and use SFTP (SSH File Transfer Protocol) or FTP-SSL (Explicit AUTH TLS). With SFTP, you can use Public Key Authentication to increase security even more by requiring a private key file and an optional de-encryption password to authenticate the FTP access.

7. Limit unsecured FTP access

If you do have to connect through regular (non-secure) FTP for some accounts (i.e. to upload photos), limit access for these accounts to a narrow set of directories. You can then use .htaccess and httpd.conf files to prevent scripts from running in these directories that can change other files and directories on the server that should not not be accessible through that FTP account.

If you have access to the httpd.conf file on your server, this is the best method to preventing scripts from running in a specific directory. Place this code in your httpd.conf file:

<directory path-to-directory-you-want-to-restrict="">
AddHandler cgi-script .php .pl .py .jsp .asp .htm .shtml .sh .cgi
Options -ExecCGI
</directory>

If you don't have access to httpd.conf, you'll have to use.htaccess. Include the following code in the .htaccess file of the directory you want to restrict:

AddHandler cgi-script .php .pl .py .jsp .asp .htm .shtml .sh .cgi
Options -ExecCGI

Because .htaccess does not support the tags, the .htaccess file must be placed in the directory you want to effect. Because of this, you need to set the permissions of the .htaccess file to 444 (read-only) to prevent modifications to the .htaccess file. You may also want to chown the file so the permissions cannot be changed. This method isn't fool-proof, but it's a good start to preventing naughty scripts from wreaking havoc.
 

Important: placing this code in a directory's .htaccess file will prevent scripts from running in that directory and all sub-directories.

8. Don't save passwords on your computer
 

Most modern computers and browsers offer the option to save passwords as a convenience so you don't have to enter your password every time. This is great most of the time, but can be a security problem because often saved passwords can be easily revealed in plain text. Anybody with access to the computer has access to the sensitive data. Even worse, someone could steal the computer and then use the saved passwords to access the sensitive data. To avoid unintended access to your Magento password or data, simply set your computer or browser to never save it— this might be a bit inconvenient, but it's a great security policy.

9. Keep up-to-date anti-virus software
 

Computer viruses and trojans can steal your data and log your key strokes. To minimize the risk of this happening, be sure to invest in reputable anti-virus software. Free anti-virus software like AVG may be great for home and personal use, but if you want indemnification or a warranty, you may want to look at commercial anti-virus software.

10. Restrict admin access to only approved IP addresses
 

You can use .htaccess to limit access to your admin area. In the .htaccess file for your admin directory, place the following code in order to block access to all IP addresses except those specifically listed:

AuthName "Protected Area"
AuthType Basic
order deny,allow
deny from all
allow from 11.111.111.11
allow from 22.2
</limit>


"allow from 11.111.111.11" blocks the specific IP address 11.111.111.11
"allow from 22.2" blocks a range of IP addresses beginning with 22.2

There is a downside to restricting access based on IP: if you travel a lot you may find this method very inconvenient as you'd have to manually add each new IP address or IP range to the .htaccess file in order to gain access.